
Data Privacy in AI Applications: What Businesses Must Know
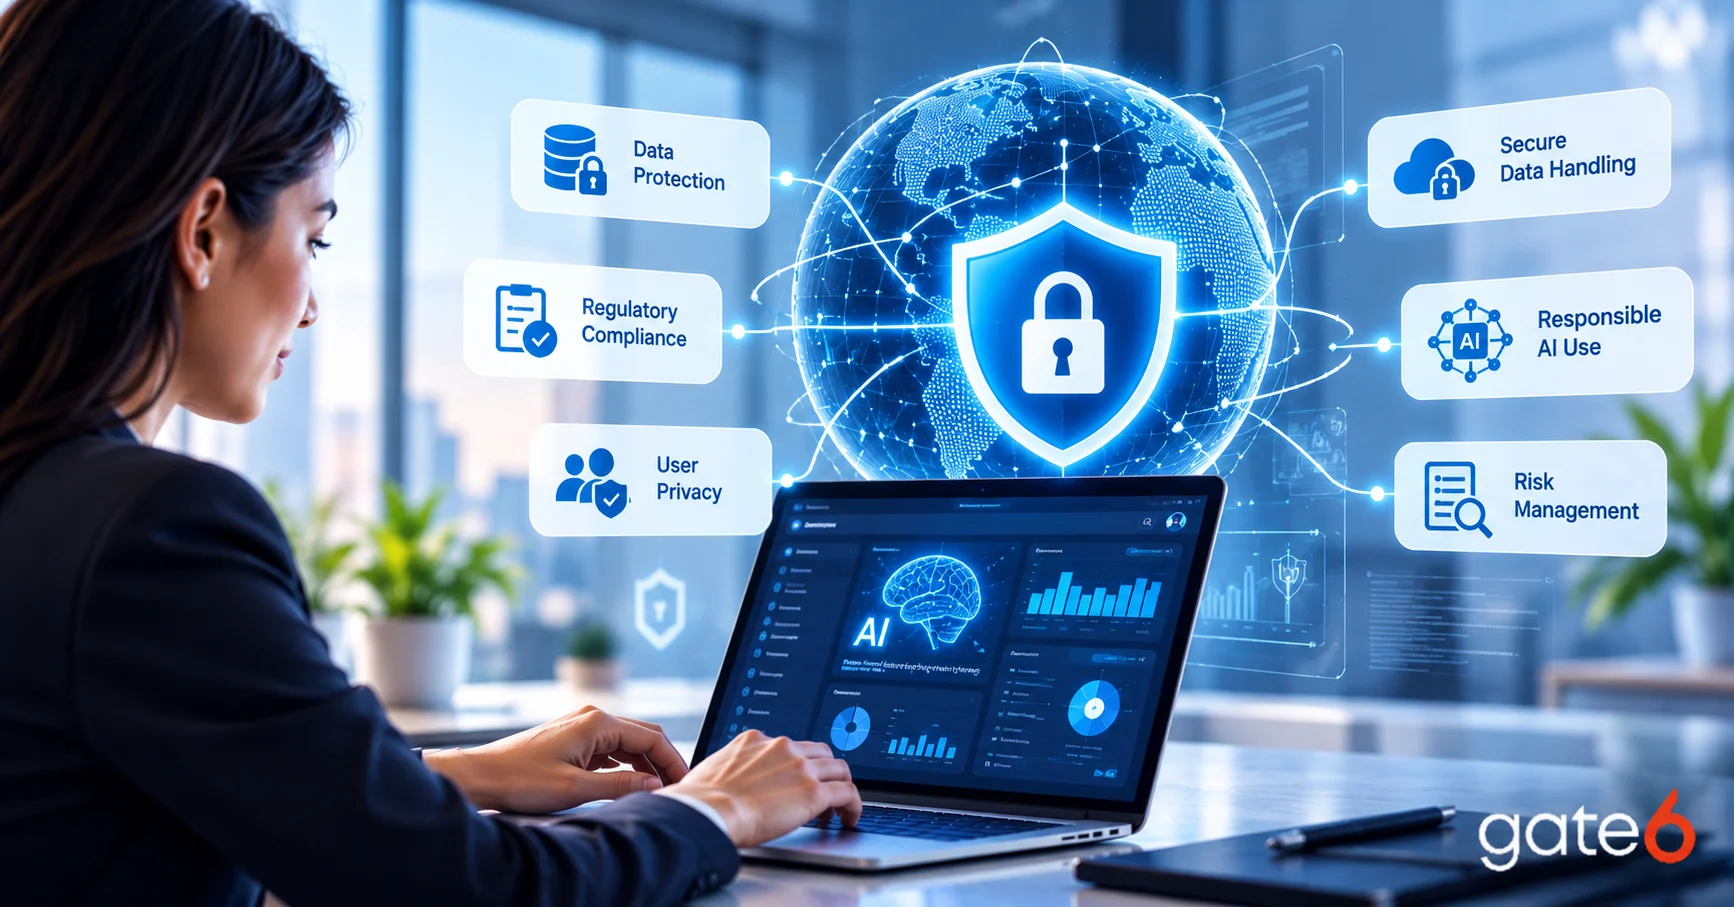
AI has become an essential part of websites, mobile apps, enterprise platforms and business workflows. As a result, these systems now depend on large amounts of data to generate predictions, recommendations, content, and automated decisions.
That creates an important responsibility for businesses. Customer information, employee records, financial details, health-related data, and other sensitive information may pass through AI systems during training, testing, and day-to-day use. Protecting this information is essential for maintaining customer trust, reducing security risks, and meeting applicable privacy requirements.
Businesses building AI-powered products need to think about privacy from the beginning. Gate6 provides AI Application Development Services that can help organizations design intelligent applications with appropriate controls for data protection, access, storage, and monitoring.
Here’s what businesses need to know about data privacy in AI applications.
Why Data Privacy Matters in AI Applications
AI systems can process information at a much larger scale than many traditional applications. They may collect data from customer interactions, uploaded documents, application activity, connected platforms, and other sources.
A privacy issue can arise if information is collected without proper controls, stored longer than necessary, accessed by unauthorized users, or shared with third-party services without appropriate safeguards.
Strong AI data privacy practices help businesses:
- Protect sensitive customer and business information
- Reduce the risk of unauthorized data access
- Support compliance with applicable privacy requirements
- Build customer confidence in AI-powered products
- Create more responsible AI systems
Privacy should be treated as a core product requirement, not an additional feature added after development.
Know What Data Your AI Application Uses
The first step toward better privacy is understanding what information an AI application collects and processes.
Businesses should identify the types of data entering the system, how that data is used, where it is stored, and who can access it. Not every piece of information needs to be sent to an AI model.
Data mapping can help teams identify sensitive information such as names, contact details, account information, financial records, or other confidential business data. This makes it easier to establish appropriate controls.
Organizations should also review whether each data element is actually necessary for the intended AI functionality. Collecting less unnecessary information can reduce privacy exposure.
Minimize the Data Shared With AI Systems
Data minimization is an important principle for AI applications. Businesses should avoid sending more personal or confidential information to an AI system than the application actually requires.
For example, an AI-powered customer support tool may need information about a support request but may not need a customer’s entire account history.
Useful practices include:
- Collect only required information
- Remove unnecessary personal identifiers
- Anonymize or pseudonymize data where appropriate
- Limit sensitive information included in prompts
- Review data requirements regularly
Reducing unnecessary data can make AI systems easier to manage while lowering potential privacy risks.
Control Access to Sensitive Information
Not everyone involved with an AI application should have access to all of its data. Strong identity and access controls help businesses ensure that employees, applications, and services can only access information required for their role.
Role-based access control can separate permissions between administrators, developers, support teams, and other users. Multi-factor authentication can add another layer of protection for sensitive systems.
Access should also be reviewed regularly. Removing outdated permissions helps reduce the chance of inappropriate access as teams and responsibilities change.
Protect Data During Storage and Transmission
AI applications communicate with databases, APIs, cloud platforms, and third-party services. Sensitive information needs protection while it is being transmitted and while it is stored.
Encryption is commonly used to protect data from unauthorized access. Businesses should also secure databases, API connections, backups, and other storage systems that handle sensitive information.
Security practices should cover the entire data lifecycle, from collection and processing to storage, sharing, retention, and deletion.
Understand Third-Party AI Services
Many businesses use external AI models, cloud providers, APIs, and software platforms as part of their applications. Each provider can introduce additional considerations for data privacy.
Before sharing business or customer information with a third-party AI service, organizations should understand how the provider handles submitted data, what security controls are available, how long information may be retained, and whether the service supports the organization’s privacy requirements.
Vendor reviews are especially important for applications handling regulated or highly confidential information.
Be Careful With AI Training Data
Training data can contain valuable information, but it can also introduce privacy concerns if personal or confidential information is included without appropriate controls.
Businesses should establish clear policies for what data can be used for model training, testing, or fine-tuning. Sensitive information should be reviewed and protected before being included in datasets.
Teams also need to understand whether an AI model is being trained on customer data or simply using data temporarily to generate a response. These are different use cases and may require different controls.
Give Users Appropriate Transparency and Control
Customers should have a clear understanding of how their information is being used within an AI-powered application.
Privacy notices and product interfaces should explain relevant data practices in language users can understand. Businesses should also provide appropriate options for managing their information where required.
Transparency can help users make informed decisions and creates greater confidence in AI-powered products.
Monitor and Review AI Data Practices
Privacy protection doesn’t end when an AI application goes live. Data flows, vendors, models, and application functionality can change over time.
Regular reviews can help businesses identify new privacy risks and verify that existing controls are still effective. Monitoring should include data access, third-party integrations, storage practices, and changes to AI functionality.
Security and privacy teams should work closely with product and development teams so potential issues are addressed early.
Build Privacy Into AI Development
Privacy should be considered during planning, architecture, development, testing, deployment, and maintenance. A privacy-first approach helps businesses identify risks before they become expensive to correct.
Organizations can combine data minimization, access controls, encryption, secure APIs, vendor assessments, monitoring, and clear data policies to create a stronger foundation for responsible AI.
Working with an experienced development partner like Gate6 can also help businesses balance AI capabilities with privacy and security requirements. AI Application Development Services can support the design and development of AI solutions with data protection considered throughout the application lifecycle.
FAQ
1. Why is data privacy important for AI applications?
AI applications can process large amounts of sensitive information, which increases the impact of a potential privacy issue. Strong privacy practices help protect information and support customer trust.
2. What types of data privacy risks can AI applications have?
Common risks include unauthorized access, excessive data collection, insecure integrations, inappropriate data retention, third-party exposure, and the use of sensitive information without suitable controls.
3. How can businesses protect personal data in AI systems?
Businesses can use data minimization, encryption, access controls, anonymization, secure APIs, vendor assessments, and continuous monitoring to reduce privacy risks.
4. Should customer data be used to train AI models?
It depends on the application, data, business purpose, and applicable requirements. Organizations should establish clear policies and assess whether customer information is necessary and appropriate for model training.
5. Is AI privacy only a technical issue?
No. Data privacy involves technology, business processes, governance, legal requirements, and user communication. Product, security, development, and compliance teams should work together to manage privacy risks.
Why Gate6 Is the Right Partner for Secure AI Solutions
At Gate6, we help businesses develop AI-powered applications with a strong focus on security, scalability, and responsible data handling. Our team works across product development and technology architecture to create solutions that address real business needs while considering data protection from the start.
We deliver:
- AI applications designed with data privacy in mind
- Secure architectures for sensitive business information
- Integration with enterprise systems and APIs
- Scalable AI solutions aligned with evolving business needs
Whether you’re developing a new AI product or adding intelligent capabilities to an existing application, Gate6 can help you build a solution where privacy and performance work together. Contact us to discuss your AI application requirements and create a secure, scalable digital product.
Let’s build AI solutions that deliver business value while treating data with the care it deserves.

Written by Bob Cody
Share post


Recent Posts

Relevant Posts
August 4, 2026


